The growing adoption of AI, cloud computing, and digital modernization is driving the exponential growth of non-human identities. Today, non-human identities outnumber human identities by a ratio of 101:1, making certificate management an increasingly critical challenge.
In hybrid, multicloud, and on-premises environments, every unmanaged TLS certificate represents a potential blind spot that can compromise service availability, increase the attack surface, and expose organizations to security and compliance risks.
Certificate Lifecycle Management (CLM) solutions help prevent breaches and protect organizations' digital infrastructure, making this a top priority for CISOs and IT leaders.
TLS certificates are a key mechanism for establishing trust in digital communications, ensuring entity authentication, and protecting data in transit.
Shorter Certificate Lifespans
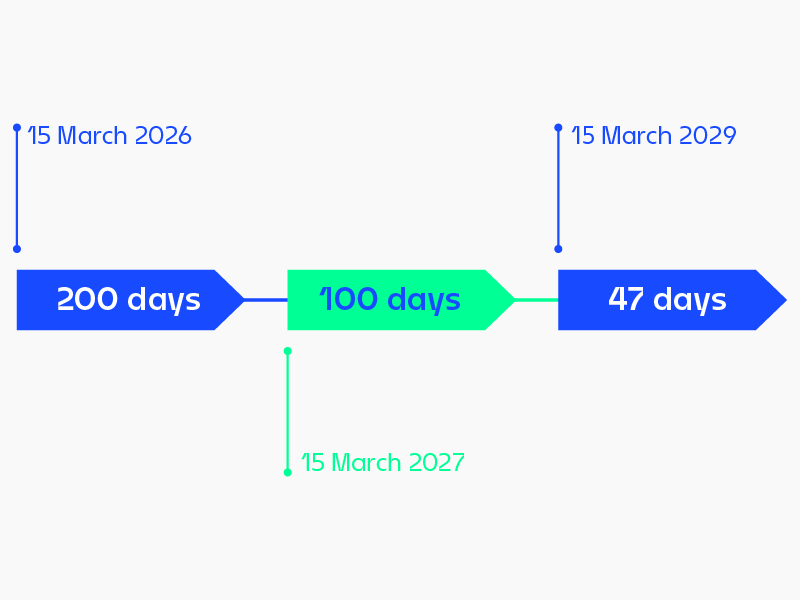
The CA/Browser Forum has approved a progressive reduction in the maximum validity period for TLS certificates through March 2029. This change will directly affect the operating model of any organization that relies on certificates to secure its communications.
With certificates requiring more frequent renewal, manual TLS certificate management is no longer sustainable. Automation is essential to reduce risk, prevent service disruptions, and ensure business continuity.
Idira Palo Alto Network
Based on Idira from Palo Alto Networks, Noesis has certified consultants specialized in implementing Machine Identity Security for Certificate Management. The solution enables:

Complete Visibility
Discovery, monitoring, and continuous validation of all TLS certificates across the organization

Compliance Assurance
Meeting audit requirements while reducing the risks associated with the manual management of certificates and keys

Efficiency & Automation
Simplification of the entire certificate lifecycle, from request to installation, with automated alerts and validation

Flexible Issuance
Integration with multiple Certificate Authorities (CAs) or use of the built-in CA

Reduced Downtime
Automated issuance, installation, and renewal of TLS certificates to reduce the risk of service interruptions

Team Autonomy
Secure, self-service TLS certificate management for developers and application owners